

Digital Identity Management Features and Enhancements
This section describes the key updates in this release:Enhanced User Lookup Options in the Care Console
With this release, Digital Identity Management offers the option to look up users by billing account ID. This new search option allows agents to locate user accounts more efficiently, reducing response times and improving the support experience. This feature can be useful to organizations with users that have associated billing accounts. To find a user by billing account ID in the Care Console, enter the billing account ID in the Search box on the Find a User page.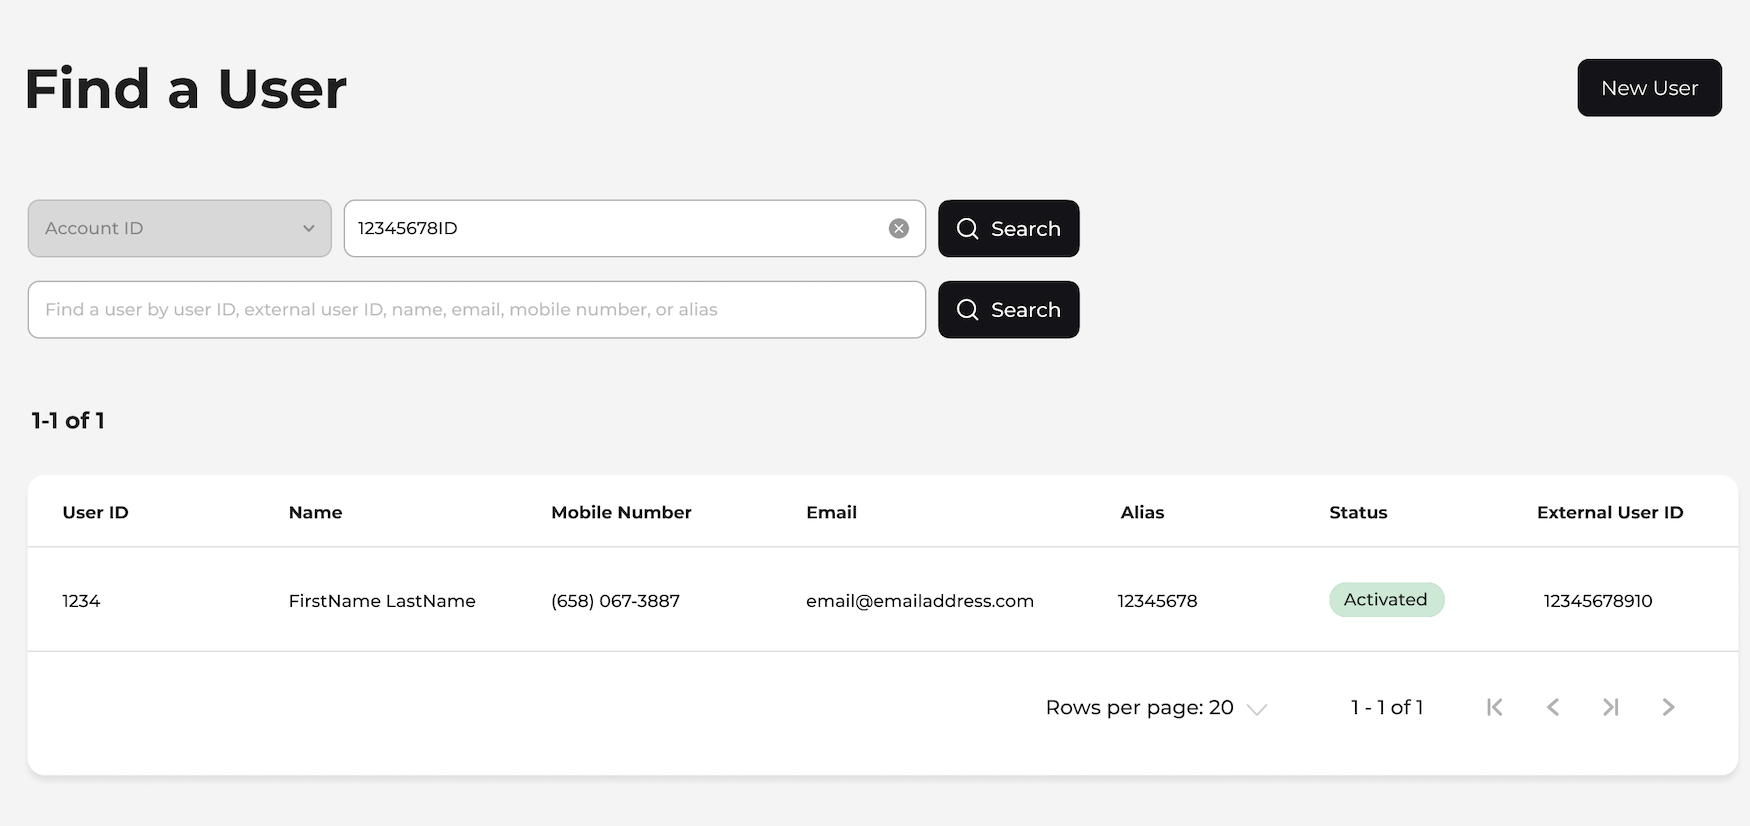
Expanded Subscription Insights in the Care Console
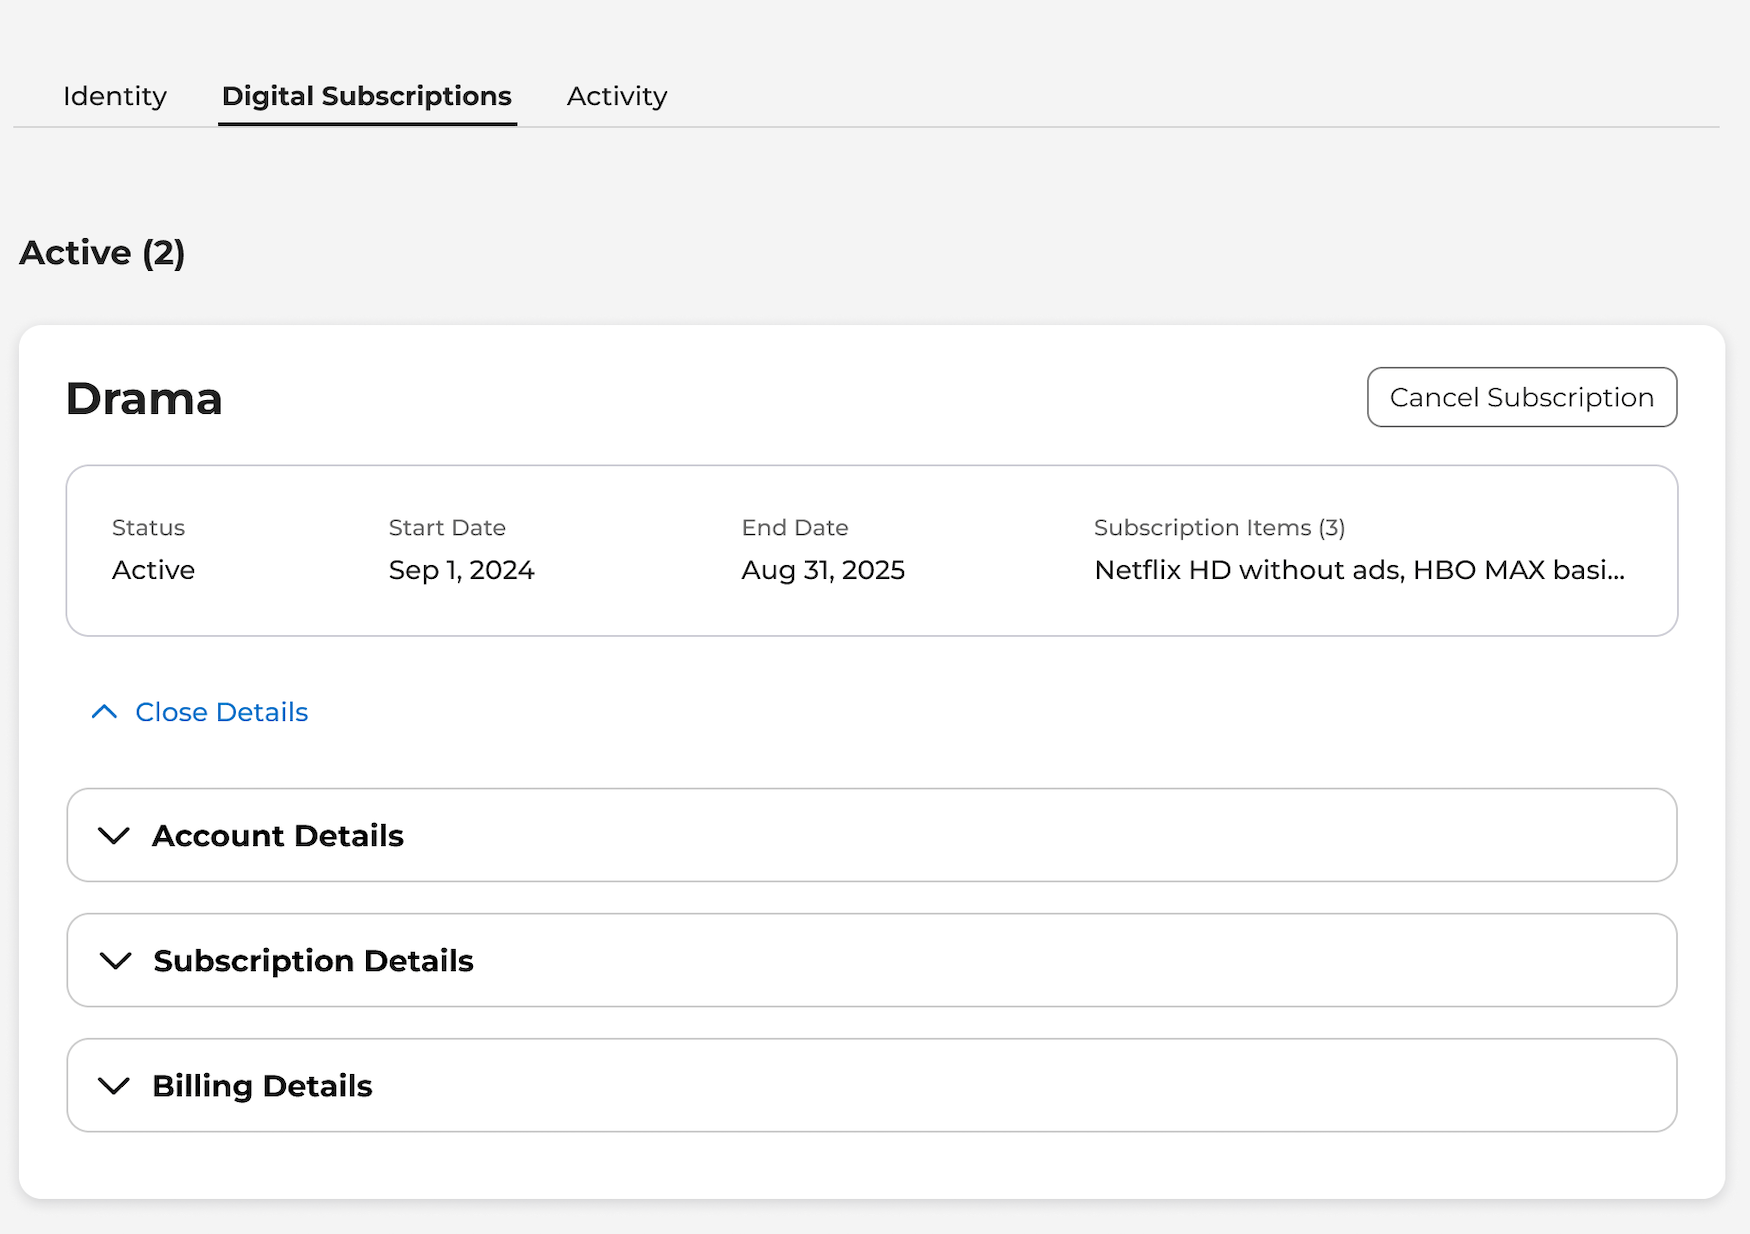
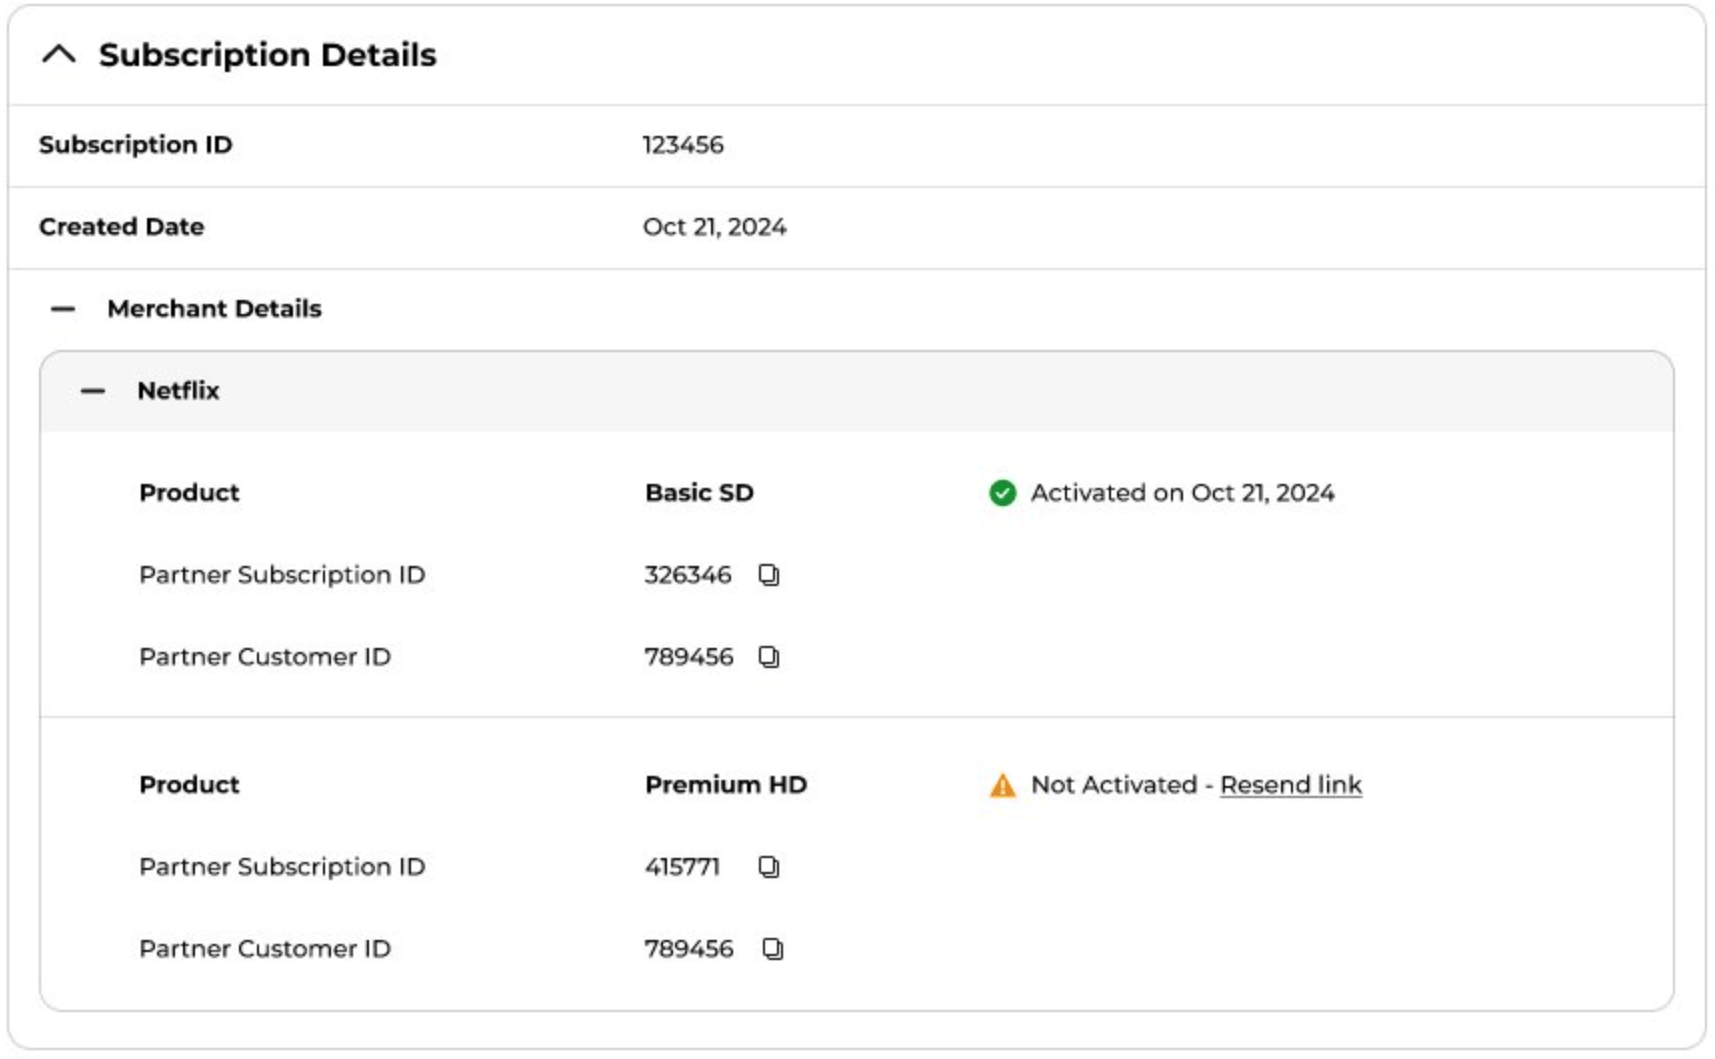
With this release, the Digital Subscription page in the Care Console has been improved to make it more user-friendly for support agents, providing easier access to additional information. This update provides agents with comprehensive subscription information, enabling them to respond to inquiries more effectively. New details include:- The user’s account ID is associated with each subscription
- Subscription item details
- Partner-related IDs for easy lookup within partner systems (if needed)
- Billing plan details, including type, date, status, and associated payment method
Flexible Impersonation API with Configurable User Consent
With this release, Digital Identity Management introduces flexible consent options so customers can configure whether consent is required or not for agents impersonating end users. The impersonation API can now be configured to either prompt users for consent or allow impersonation without it, enabling smoother support for cases where consent is not mandatory. To use this enhancement, configure the **system,oidc.impersonation.**consentRequired app setting according to your organization’s requirements.Enhanced External IdP Federation API: Expanded Parameter Support
The external IdP federation Process API now supports additional parameters,prompt and ui_locales, alongside login_hint. These parameters provide more context to external IdPs, enabling a smoother, more personalized user experience. This makes federated authentication interactions more intuitive and aligned with user preferences.
Use these parameters as needed to optimize the experience with external IdPs.