

Authentication Using an External Identity Provider (IDP)
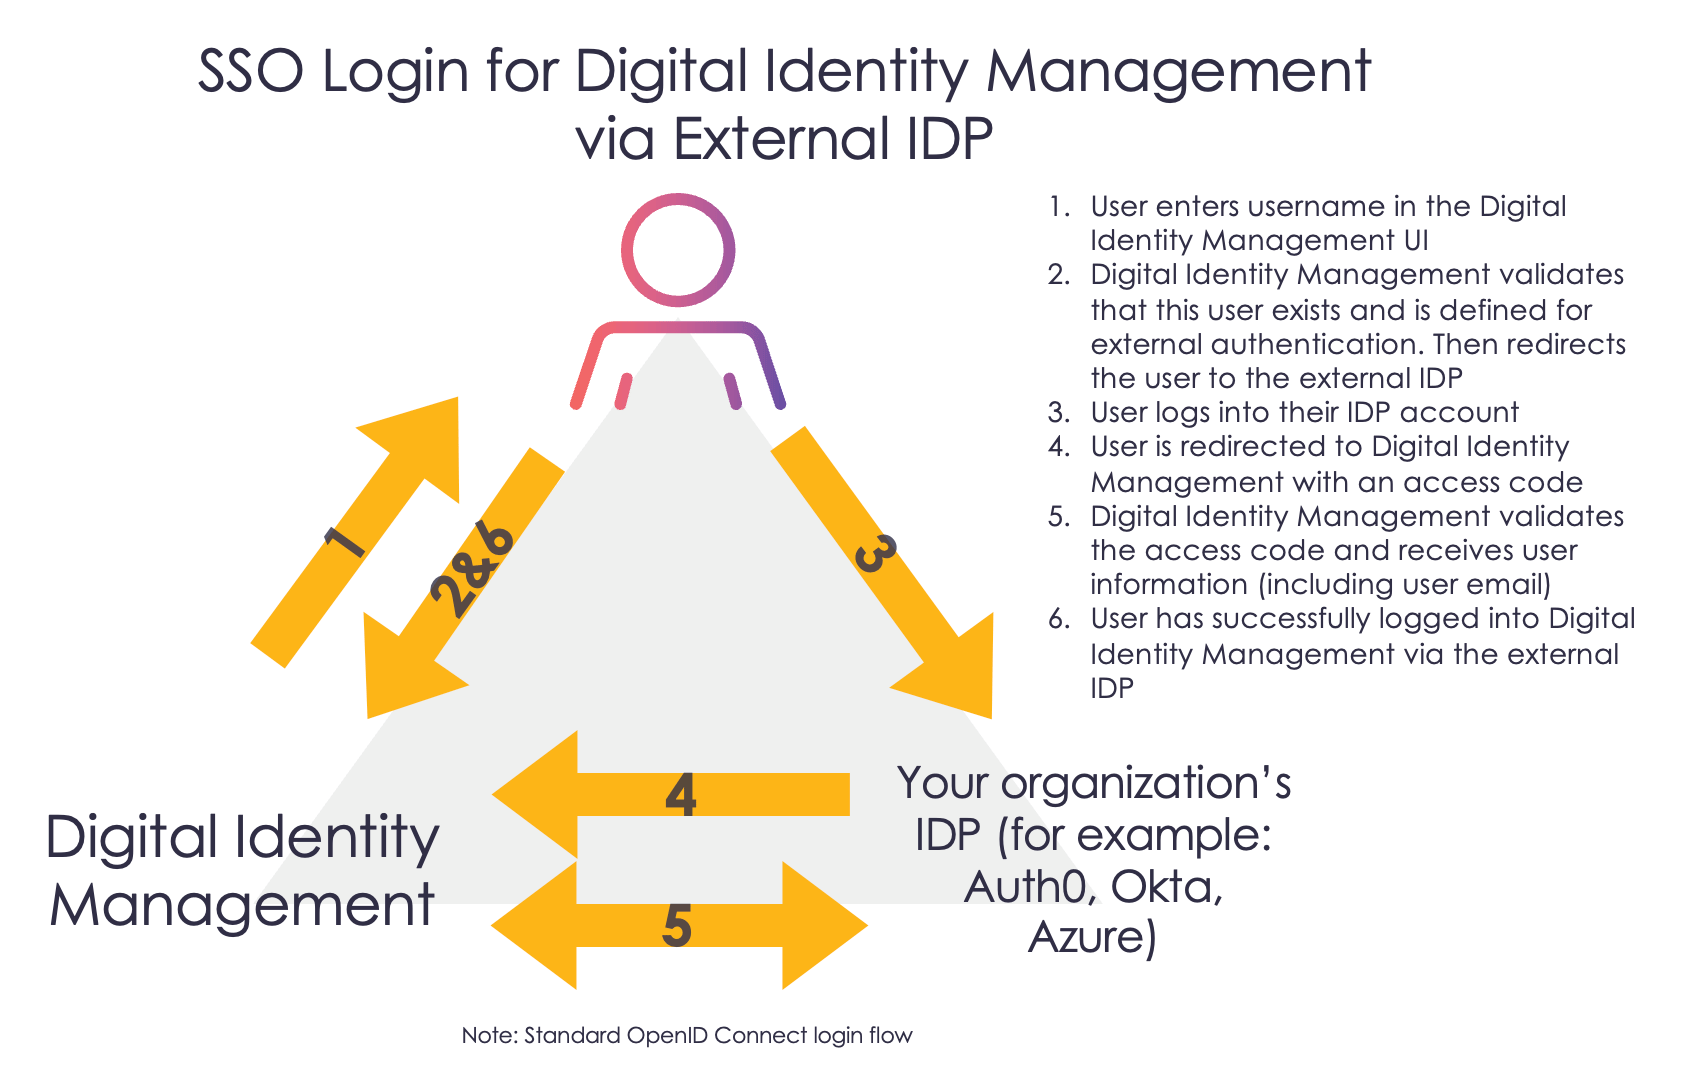
Digital Identity Management supports external identity provider (IDP) federation. Organizations can use their own external IDPs for user authentication. Users can leverage the same credentials that they already use for the external IDP. If users are already logged in to the IDP, they don’t have to log in again to access the end user application.
Optionally, organizations can request to use their own external user authentication via their Identity Provider using OIDC-standards.
Once the external user authentication single sign on is set up, the users can use their external IDP credentials to access the Digital Identity Management UI.