

/oidc/authorize endpoint, and then transmits the original (un-hashed) string, called the code verifier, in the final /oidc/token request. Digital Identity Management checks that the verifier hashes to the challenge, to prove that the app making the /oidc/token request is the same that made the previous /oidc/authorize request.
Flow Diagram
The diagram below represents the communication flow between the key actors using the Authorization Code Grant with PKCE: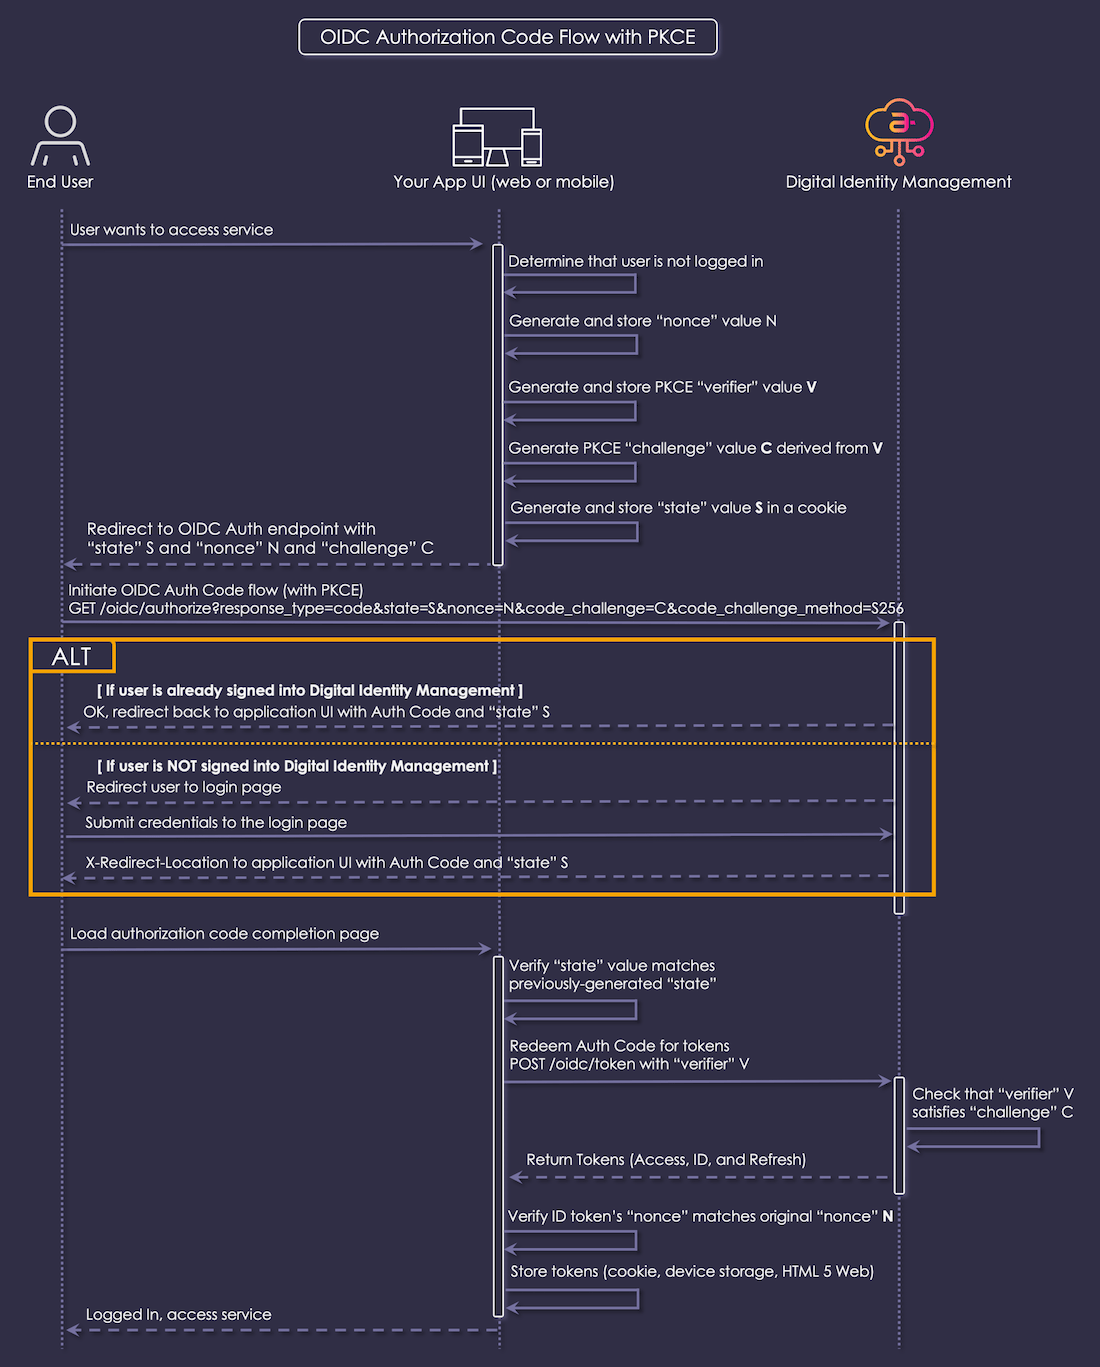
Interaction Steps
The interaction steps between each actor in the flow are as a follows:- The user visits or opens your application to access a secured service.
- Your app determines that the user is not currently signed in.
-
Your app generates and stores a cryptographically random
nonceASCII string. This will be used to validate the OIDC response, and must not be guessable by an outside attacker. -
Your app generates and stores a cryptographically random verifier string. The string must consist exclusively of:
- lowercase and uppercase letters
- numbers
- period, underscore, hyphen, or tilde punctuation characters To produce the string, we recommend that your application generates at least 32 bytes of random binary data, then encodes it using the base64 URL scheme. Store this for later.
- Taking the PKCE Verifier string generated in the previous step, your application must compute the SHA-256 hash of the string and base64url-encode it. This value will be used immediately in the OIDC redirect.
-
Your app generates and stores a cryptographically random
stateASCII string. This will be used to validate the OIDC redirect back to your app, and it must not be guessable by an outside attacker. If your application is web-based, you may store this value in a cookie. -
Your application redirects the end-user’s browser (or in a mobile application, opens a browser window) to Digital Identity Management’s
/oidc/authorizeendpoint with the following HTTP GET query parameters:
-
The user’s browser loads the
oidc/authorizeURL as per the HTTP 302 response from step 7. Digital Identity Management inspects the browser cookies to determine if the user is already authenticated. The next step depends on whether the user is already authenticated in Digital Identity Management. -
(Conditional) If the request is not valid, or if the user is already authenticated and re-authentication is not being forced, then Digital Identity Management immediately responds with an
HTTP 302 Temporary Redirectto theredirect_uriwith certain HTTP Query parameters. Skip steps 10 through 12 and go to step 13. -
(Conditional) If the user is not authenticated, then Digital Identity Management redirects them to the configured IdP Portal (that is, the central sign-up/sign-in page for all of your registered RPs).
-
In the most conventional use case, the user authenticates with Digital Identity Management’s
POST /sesion/startAPI. This API invokes Digital Identity Management’s multi-step Authenticate User Process. Alternatively, the user may need to first onboard with the Onboard User with Email or Mobile Process, which is invoked by thePOST /proces/start/{processName}API. This and other variations are not included in the flow diagram. -
Eventually, whether from a /session/start or other Process call, and potentially after several more steps (for example, to satisfy multi-factor authentication rules, if enabled), the user is authenticated. The final HTTP response from Digital Identity Management includes a special
X-Redirect-Locationheader with a URL constructed from theredirect_uriparameter provided by the RP in step 7. The IdP then redirects the browser to that location. -
The user’s browser loads a URL which Digital Identity Management has constructed from the
redirect_uriparameter, to which the following HTTP Query parameters will have been added: -
Your app checks the
statevalue in the request against the originalstatevalue stored in a cookie or HTML Web Storage. If there is a mismatch, a cross-site request forgery (CSRF/XSRF) attack is suspected, and the operation must be aborted with an error. -
Your app makes a background call to Digital Identity Management’s
POST /oidc/tokenendpoint to redeem the authorization code for OIDC tokens:Unlike in the base Authorization Code Flow (as described in the SSO for Web Apps with a Back End topic), you do not pass any client credentials in the PKCE version of this flow. The body of the request is of typeapplication/x-www-form-urlencoded. -
Digital Identity Management checks that the
code_verifiersupplied in the token request hashes to thecode_challengesupplied in the authorization request (step7). -
If all parameters are correct and the Authorization Code is valid, Digital Identity Management replies with a JSON payload that contains the requested token(s). The payload is of type
application/json, and it consists of a JSON object resembling the following:The fields of this JSON object are as follows:
- Your app decodes the ID token, and inspects the payload to make sure the
noncekey is present and its value matches thenoncevalue N from the original request (generated in step 3). If not, a replay attack is suspected and the operation must be aborted with an error. - Your app stores the tokens in an appropriate place (for example, cookies or HTML5 Web Storage for a web UI, or device storage for a mobile app).
- As long as the access token remains valid, the user remains authenticated. For more details on how to refresh (that is, get replacement) a token, refer to the Refreshing Tokens topic.