

Accounts, Associations, and Groups
Digital Identity Management enables account and service sharing by way of associations between Digital Identity Management Users, Digital Identity Management Groups, and Digital Identity Management Accounts (which contain Subscriptions and Features). See the intro sections inAssociate Billing Account and Share Access to Account, Subscription, or Feature Processes for more information. But here are a few basic reminders: Customer Accounts and Services as Digital Identity Management Accounts, Subscriptions, and Features- External accounts and services are mapped to Digital Identity Management Accounts, Subscriptions, and Features (A/S/F) entitlement entities.
- Each Account owns or contains Subscriptions, and each Subscription can contains its own Features.
- Mapping of external record data to Digital Identity Management entity data is based on an integration between Digital Identity Management and the service provider’s external Billing / Operations Support System (B/OSS).
- When a user associates their account (i.e., when the Account/Subscription/Feature hierarchy are provisioned in Digital Identity Management), that account is automatically associated to the User, and to a Group in which the User is the “Group Primary.”
- Either the Digital Identity Management User selects one of their existing Groups (if any exist), or a Group is automatically created and the A/S/F is associated to it.
- The Group to which an A/S/F is associated is sometimes referred to as the “Account Group”, but it’s technically known as a User Group first a foremost.
- The Digital Identity Management User who owns the A/S/F and the Group is designated the “Group Primary” or “Primary User”
- When the Primary User invites other Digital Identity Management Users to share access to an Account or Service, they select specific Digital Identity Management Accounts, Subscriptions, or Features (not necessarily all or even more than one entity).
- The Primary User also sets permissions for the invitee User to have (either consumption, management, or both).
- When the invitee accepts, their Digital Identity Management User entity is added to (i.e., associated to) the Digital Identity Management Group and the specified Accounts, Subscriptions, or Features.
- In order for any Digital Identity Management User to have access to an Account, Subscription, or Feature, they must:
- Be associated to the Digital Identity Management Group
- Be associated directly to the Specific Account, Subscription, or Feature
- When a user signs into an application, that application can call various connect API to check and see if the user is associated to the relevant entitlement entity, and then grant them access to that service.
Process Flow
This flow describes the Process at a high level. Preconditions- The user is currently authenticated
- The user has at least one account/service associated to their User ID, and they are the Primary User (owner).
- The target Digital Identity Management User is in at least one of the current user’s Digital Identity Management Account Groups
- The current user selects to remove another Digital Identity Management User from their group.
- The UI prompts the user to select a target user.
- The client may need to leverage Digital Identity Management APIs to retrieve the relevant Group information (e.g., to what Groups is the current User associated, and what other Digital Identity Management Users are in those Groups)
- The user selects a target user to remove.
- The client must provide the selection using the target user’s Digital Identity Management User
idproperty.
- The client must provide the selection using the target user’s Digital Identity Management User
- (Conditional) If the user and the target user are in multiple Groups together, then Digital Identity Management prompts the client for a Group selection, and the UI prompts the user to select the specific Group
- (Conditional) The user specifies the Group.
- Digital Identity Management removes the target User entity from the Group.
- The target User entity is disassociated from the specified Digital Identity Management Group.
- All associations between the target Digital Identity Management User and accounts or services from the Group are removed.
- The target user is not in any of the current user’s groups.
- This current user does not have Primary or Admin permissions for the specified group.
Settings
This Process currently has no relevant settings that configure the Process API response or Process logic/behaviour. However, additional settings are coming in future releases.User Journey Diagram
This diagram illustrates the standard user journey using the Remove User from Group Process. [product: dim]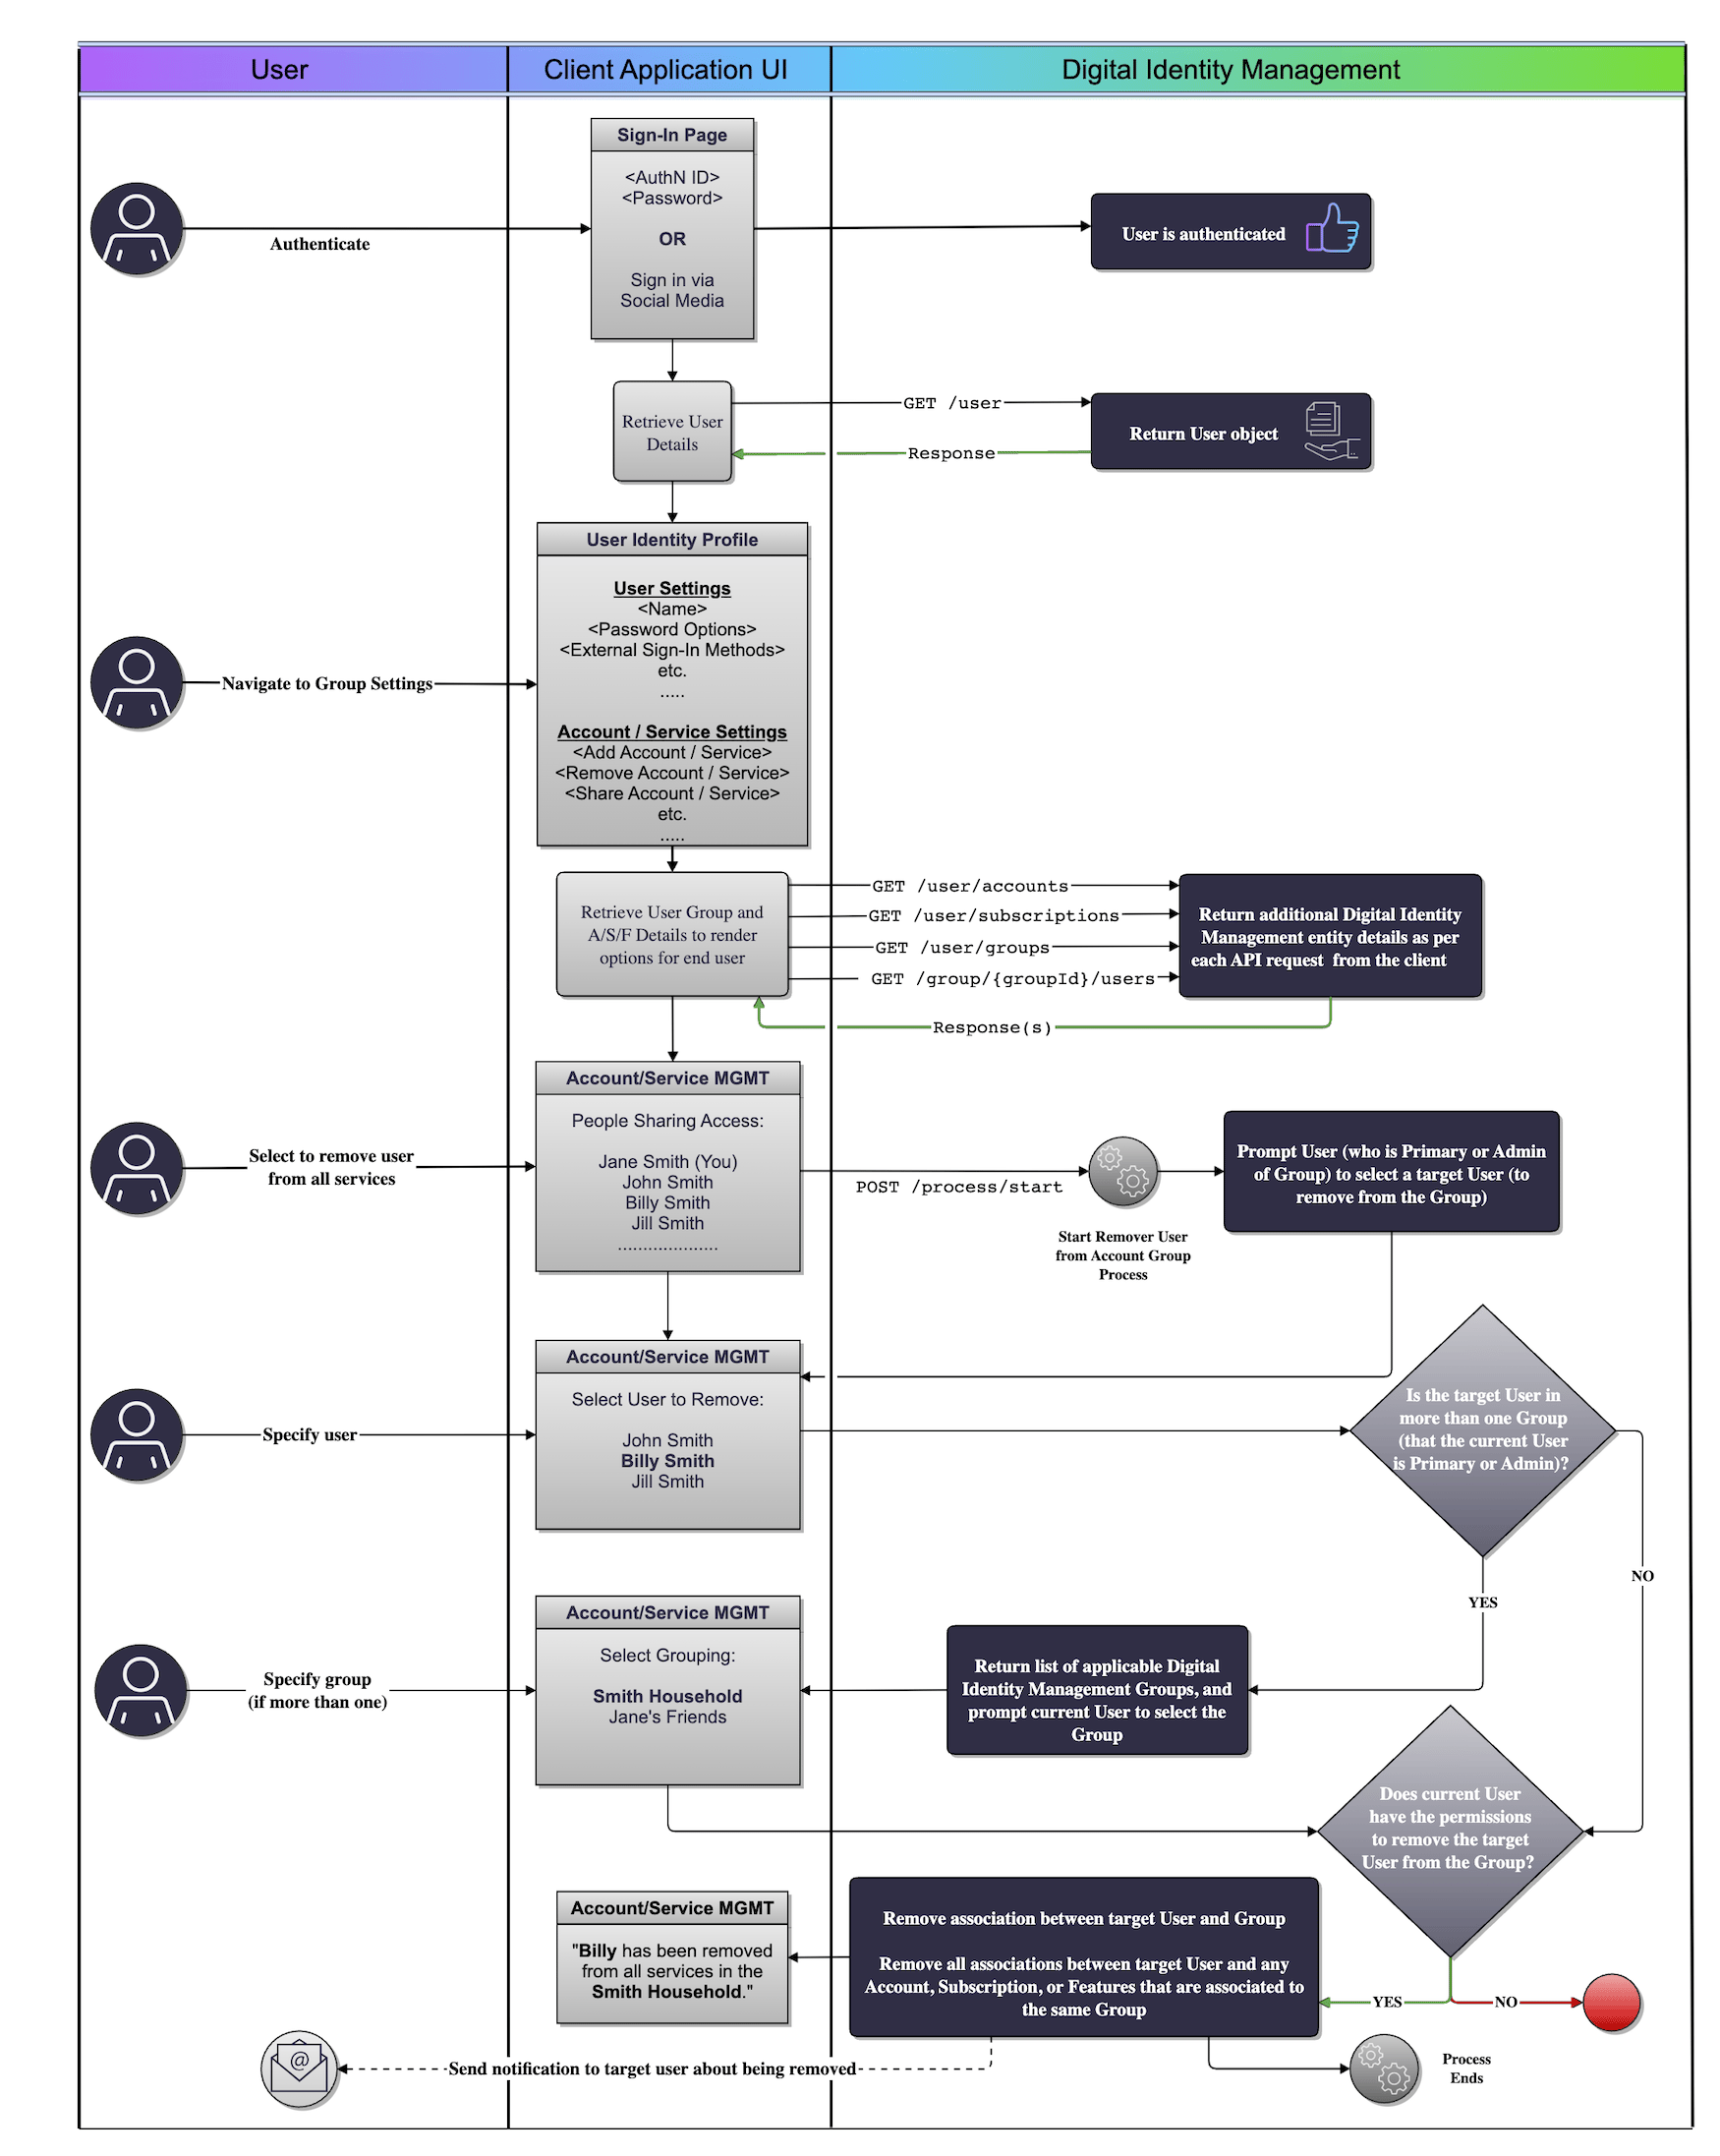
Use Cases
The following use cases provide guided API walk-throughs of this Process for client developers:- Remove user from group (single group)
- Remove user from multiple groups (multiple groups)
- Remove user errors
- Remove user from group
- Remove user from group (multiple groups)
- Remove user from group errors