

Multiple Process Orchestration
Some user journeys only need one Process or standard REST API to complete a task. Other user journeys are multi-step, dependent processes linked together with action tokens. The Digital Identity Management Process framework manages the action tokens and how they are linked together and executed.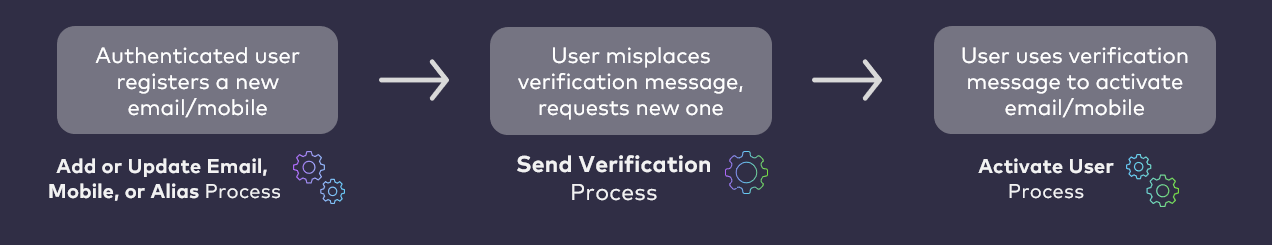
Resend Process vs Resend API
This process is functionally similar to – but distinct from – the PUT session/token API. See the following table for more details:
The Send Verification Process generates and sends a new action token to the user. Conversely, the PUT session/token API resends an existing token (updated value). Additionally, the Resend Verification Process doesn’t require a PKAT but instead needs an email address or mobile number.
This Process is beneficial where the client doesn’t have a PKAT that corresponds to an issued action token. This typically occurs when an authenticated user registers a new or additional email/mobile number to their profile (using the Add/Update Email, Mobile, or Alias Process Process). At the Process end, if the user closes the client application or browser, then the client loses the PKAT. Therefore, if the user misplaces their link/code, and they return to their profile at a later date, they can select send new link/code option from the UI, and the user’s email or mobile is sent to the POST /process/start/{processName} API request.
Add the AuthN ID to the Initial Request
Like most Processes, this Process is initialized by the Process Start API. In most use cases, the Process Start API optionally consumes no payload, and responds with a request for the data it requires to finish its task. However, the Send Verification Process needs the client to add the required parameter, the authentication identifier that needs to be verified, along in the initial request. The client can provide the target email address or mobile number in the initial request body:Process Flow
This flow describes the Send Verification Process at a high level. using the happy path flow: Preconditions- The user is authenticated in Digital Identity Management.
- The user has an email address or mobile number pending verification.
- The user navigates to their email/mobile management section of their profile (or client UI equivalent), and selects to send a verification message to a given email/mobile.
- The
GET /userAPI returns the Digital Identity Management User entity to the client. This entity includes anattributesobject wherein all of the user’s registered authN IDs are listed, including each authN IDs Status in Digital Identity Management. - The client UI can read the status and display a message or icon that signifies that status to the user.
- The
- Digital Identity Management sends a verification message to the email address or mobile number.
- The message contains a token redirect URL and/or a One Time Passcode (OTP).
- When the user redeems this token, it will trigger Activate User Process.
- Verification token is sent out to the unverified email/mobile.
- Authentication identifier not provided. The process was invoked without any authN ID.
- Invalid authentication identifier. The specified value is not a valid authN ID.
- Authentication identifier not found. The specified authN ID is not associated to this user.
App Settings
Manage app settings in the Admin Portal and configure your tokens from the Admin > Authentication > Tokens pages.Use Cases
- Send new verification link or OTP
- Sending verification errors
- Send a new verification message
- Send Verification Errors